One Breach, Four Rulebooks. Which One Decides What You Get Told
The same incident can be governed by a state statute, a health rule, a lender's rule or a securities filing, and each one gives you a different letter on a different clock.
Pinned by Josephine Lachance5 min read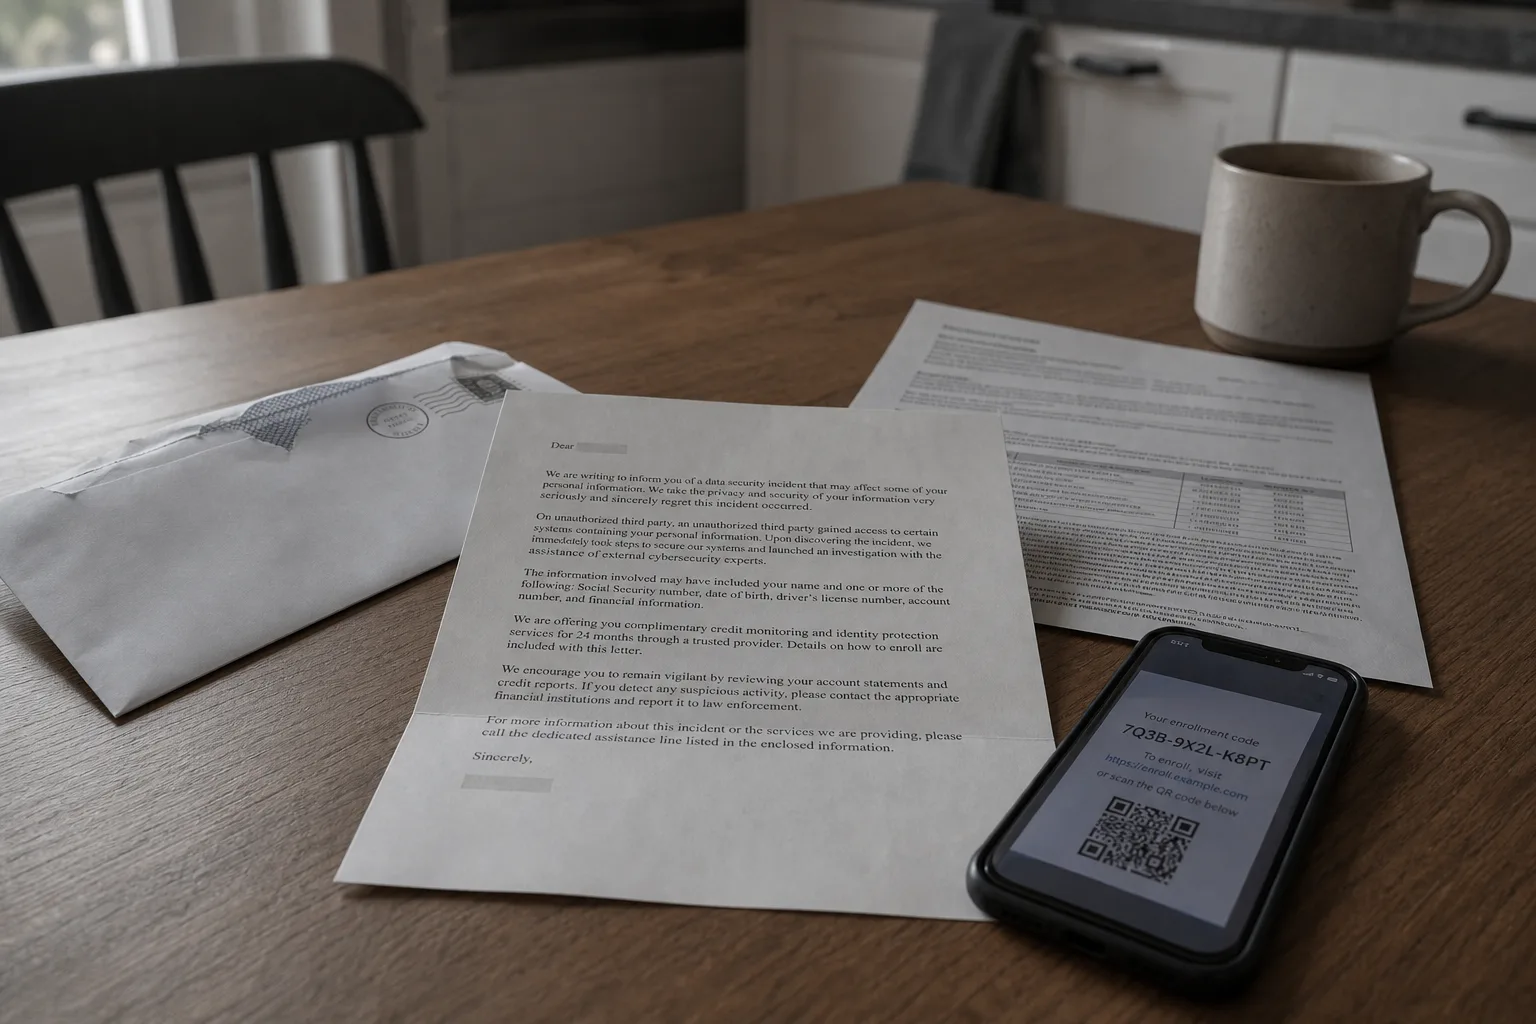 A breach notification letter on a kitchen table beside its opened envelope showing the postmark, a printed regulatory filing, and a phone displaying a photog...
The letter in your hand was not written for you. It was written to satisfy a specific rule, by a lawyer who knew exactly which rule applied, and the wording you find vague is usually vague on purpose because the governing standard did not require more. That is the useful way to read it. Once you know which rulebook the sender was answering to, you know what you are owed, how long the company had before it wrote, and which follow-up question it is actually obligated to answer. Four different regimes could be behind the same envelope, and several of them changed recently.
The state statute is the floor, and it is fifty floors
Every state has a breach notification law, and the company that lost your data is answering to the law of the state where you live, not where it is headquartered. That is why two households on either side of a state line get letters with different content about the same incident. State laws set the trigger, usually a defined category of personal information such as a Social Security number, a driver's license number, a financial account number with the credential that operates it, and increasingly biometric data and health information held outside a hospital. What falls inside that definition decides whether you hear anything at all.
The changes worth knowing are mostly about speed and about who else gets told. A number of states have replaced the old open-ended standard, notice without unreasonable delay, with a hard outer limit measured in days, and several now require a parallel report to the state attorney general once the affected count crosses a threshold. Those attorney general filings are frequently posted publicly, which matters to you practically: the report a company files with a regulator is often more specific about what happened than the letter it sent to your mailbox on the same day.
The other recent shift is remedy. Credit monitoring used to be discretionary, a goodwill gesture priced by the vendor. In a growing set of states it is mandatory when Social Security numbers are exposed, with a minimum term written into the statute. So when a letter offers you twelve months and mentions no term at all in the fine print, the question is not whether twelve months is generous. The question is whether your state sets a floor of twenty-four, and whether the company is quietly complying with a weaker jurisdiction's minimum.
Health data now travels under two different rules
If the sender is a hospital, an insurer, a lab, a dental practice or a billing company working for one of them, the governing standard is the federal health breach rule that sits alongside HIPAA, administered by the Department of Health and Human Services. Its shape is distinctive. The outer deadline for notifying individuals runs to sixty days from discovery, large incidents draw media notice and a prompt federal report, smaller ones can be logged and reported annually, and the letter itself must cover a prescribed set of points including the categories of information involved, what the entity is doing about it, and what you should do.
What changed is the other route. Health data collected by apps, wearables, direct-to-consumer testing services and wellness platforms generally sits outside HIPAA entirely, and the Federal Trade Commission, which oversees consumer data practices and unfair or deceptive conduct, has updated its separate health breach rule to make clear that it reaches those products and that a breach is not limited to a hacker. Unauthorized disclosure counts. An app that shipped your data to an advertising platform without your say-so is inside the rule's scope, and the notice duty attaches. That is why letters have started arriving from services that never looked like healthcare.
The practical difference between the two health routes is where you complain. Under the HIPAA-side rule you have a federal complaint channel against the covered entity. Under the consumer-side rule your leverage runs through the FTC and your state attorney general instead. Same category of data, same feeling of exposure, two different desks. Identify which one applies before you spend an afternoon writing to the wrong agency, and note the sender's exact legal name from the letterhead, because the entity that owes you notice is often not the brand name on the app.
Banks, lenders and the thirty-day rule that used to not exist
Financial institutions have been governed for years by a safeguards standard requiring a written information security program, but for most of that period there was no affirmative federal duty to report a breach to a regulator on a fixed clock. That gap closed. The safeguards rule now carries a notification requirement running to the FTC within thirty days of discovering unauthorized access above a defined number of affected consumers, and the definition of a covered financial institution is broader than most people assume. Mortgage brokers, auto dealers arranging financing, tax preparers, payday lenders and collection agencies all sit inside it.
For you, the value is corroboration. A regulator-facing report is filed on a shorter clock than most consumer letters, and it is filed by name. If a tax preparer or a dealership tells you on the phone that nothing was really lost, and a report exists, the two accounts can be compared. Ask in writing whether a notification was submitted, on what date, and under which rule. A company that has filed will usually say so, because saying so is the answer that helps it. Silence in response to a written question is itself a piece of record.
The public company timeline, and why the news beat your letter
Publicly traded companies now carry a disclosure duty that has nothing to do with protecting you and everything to do with informing investors. A material cybersecurity incident goes into a current report with the Securities and Exchange Commission within four business days of the materiality determination, which is a much faster instrument than any consumer notice regime. That is the reason you sometimes read about a breach in the financial press weeks before an envelope arrives, and the reason the two accounts differ in tone. The investor filing describes scope and operational effect. Your letter describes data categories and a monitoring enrollment code.
Read both. The filing frequently names the date of discovery and the date containment occurred, and those two dates are the ones your own letter is least likely to contain. Print the filing, note the date you retrieved it, and keep it with the letter. If the gap between discovery and your notification runs past your state's outer limit, you now have the arithmetic in hand rather than a suspicion, and the attorney general's office is the correct recipient for that arithmetic.
The record that survives the phone call
Start a single file the day the letter arrives, and put the envelope in it, postmark visible, because the mailing date is the fact most often disputed later. Photograph the letter including the reference number, the enrollment code and any expiration date on the monitoring offer, then note the deadline separately somewhere you will actually see it. Every conversation after that goes into writing, ideally by email to a named person, ideally repeating what you were told back to them. Ask for the discovery date, the specific data elements tied to your record, and the statute the notice was issued under.
Those three questions are the ones that convert a form letter into an account you can rely on months later, when a fraudulent account opens or a return is rejected and someone asks when you first knew. Written answers hold. Memory of a call does not, and the file you built in the first week is what makes the rest straightforward.
Posted under Innovation